Passkeys Explained: A Different Way to Sign In Online

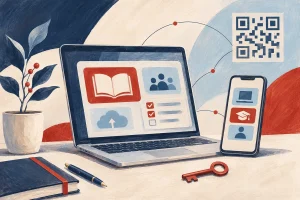
Signing in to an account usually starts with a familiar question: what was the password? Passkeys change that experience. On a supporting service, the user may confirm a sign-in using a device’s screen lock, such as a PIN, fingerprint or face recognition.
According to the FIDO Alliance’s explanation of passkeys, the system uses a pair of cryptographic keys. The service holds a public key, while the corresponding private key is used by the user’s authenticator. The private key is not sent to the service as a password would be.
Why the website matters
Passkeys are designed to work with the correct website or application. That binding helps resist phishing attempts that depend on persuading someone to type a reusable password into an imitation sign-in page.
This does not make every interaction around an account trustworthy. A suspicious message can still try to persuade someone to send money, reveal other information or change account settings. A stronger sign-in method addresses an important risk, but it does not make judgement unnecessary.
Where a passkey is kept
The experience depends on the provider and device. Some passkeys can be synchronised through a credential provider so that they are available on more than one device. Others are tied to a particular device or security key. Those differences matter when replacing a phone, sharing equipment or moving between operating systems.
Before switching an important account, read the service’s recovery instructions. Check what happens if the usual device is lost and whether another approved sign-in method is available. Follow the provider’s own setup process rather than instructions supplied in an unexpected message.
A practical first step
For someone trying passkeys for the first time, a sensible approach is to understand one account’s settings carefully. Confirm where the passkey will be stored, how additional devices work and how to review or remove a passkey later.
The appeal is straightforward: fewer passwords to remember and a sign-in process designed to resist common phishing techniques. The most useful setup is one the account holder understands well enough to manage both on an ordinary day and when a device needs replacing.